Operations & Lifecycle · 4 Oct 2026 · 5 min read
Live maintenance: approve the system state, not just the task
Maintenance approval should account for temporary capacity, control dependencies and recovery—not only the equipment being serviced.
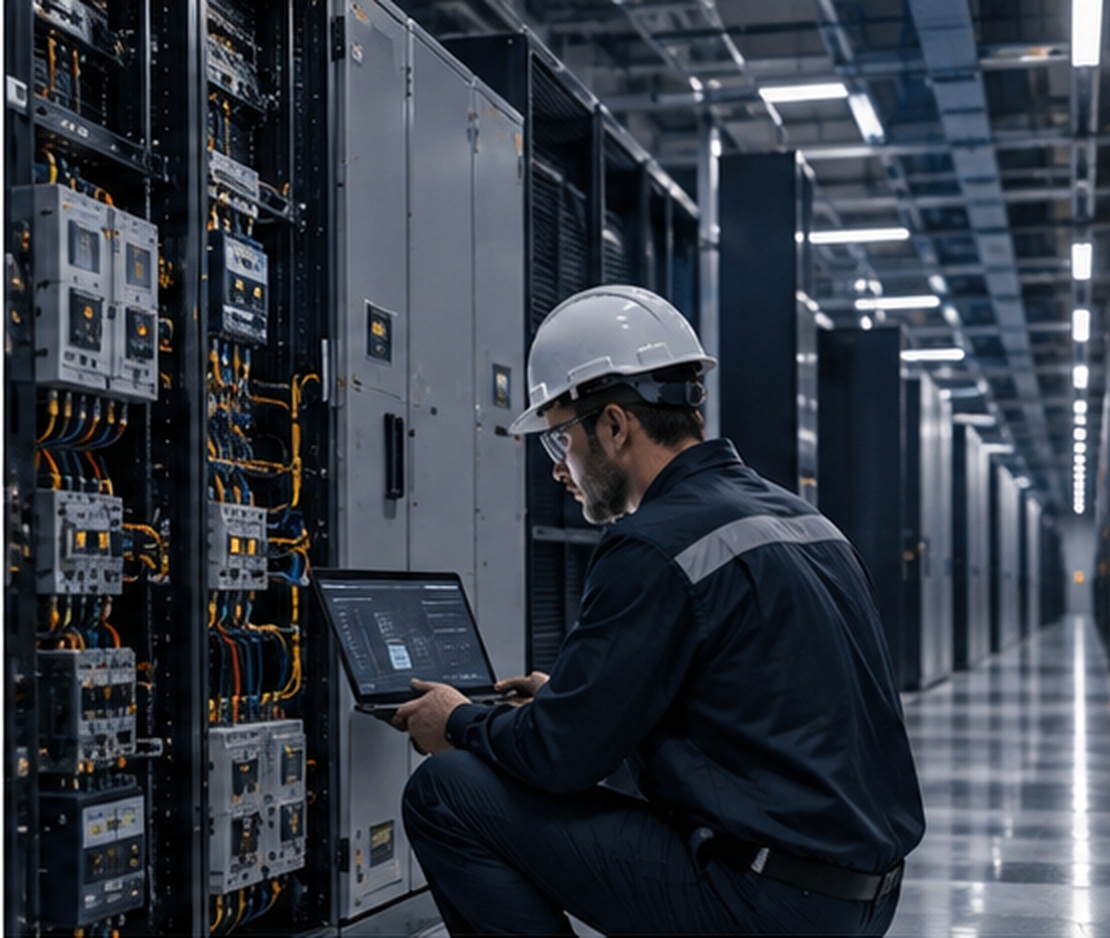
The decision hidden inside a maintenance approval
An infrastructure owner can approve a routine maintenance task without explicitly approving the operating condition it creates. The work order describes the equipment, the contractor and the expected duration. It may say much less about the facility that must remain available while that equipment is isolated.
That gap matters when approving this quarter’s maintenance windows. Demand may have changed since the procedure was written. Control logic may have been revised. Equipment expected to provide standby capacity may now carry a permanent load. A familiar task can therefore create an unfamiliar exposure.
Here, maintenance in an operating facility means safely isolating equipment while other systems continue serving the load. It does not mean working on energized equipment or bypassing safety requirements.
The executive decision is not simply whether the task is necessary. It is whether the temporary operating condition is understood, acceptable and recoverable. That decision needs an accountable owner, not just a completed work order.
Review the system that remains available
Equipment-level maintenance plans rarely describe the full service boundary. Taking a cooling unit out of service affects available heat-removal capacity, but the consequence also depends on distribution, pump operation, control sequences and the location of the active load.
The same principle applies to electrical and network infrastructure. A nominally independent path may share an auxiliary supply, control connection or physical route. Removing one asset can expose a dependency that normal operation conceals.
The review should therefore describe the remaining system, not merely the isolated asset. Which services remain available? At what operating limits? Which protective functions and alarms remain effective? What other work must be excluded during the window?
Useful evidence includes current load information, verified equipment availability and controlled documentation of relevant interfaces. Historical design intent alone is insufficient.
An owner should also distinguish spare capacity from usable capacity. Capacity that cannot reach the affected load, or cannot respond within the required time, should not be treated as protection for the maintenance window.
Make temporary risk an explicit business choice
Maintenance can leave a facility with enough capacity to serve its load but less tolerance for another failure. Those are different conditions. Describing both as “operational” hides the decision the owner is actually making.
The maintenance approval should state what changes during the window: reduced redundancy, tighter environmental margins, restricted load growth or dependence on a specific recovery action. It should identify the conditions that would make proceeding unacceptable.
There is a real trade-off. Deferring maintenance can preserve today’s operating configuration while allowing equipment condition, supportability or compliance obligations to deteriorate. Proceeding can reduce lifecycle risk while temporarily increasing exposure to interruption. Neither choice is automatically safer.
The comparison should consider the consequence of delay alongside the consequence of an additional failure during the work. Where uncertainty is material, options may include a narrower scope, a different window, temporary capacity or a planned service restriction.
The point is not to eliminate all temporary risk. It is to prevent unpriced, unowned risk from entering the operating plan by default.
Assign authority across the interfaces
Multiple parties may be competent within their own scope while nobody owns the complete maintenance condition. An equipment specialist understands the asset. A controls contractor understands the sequence. The operations team understands current demand. Each can still hold an incomplete picture.
Before approval, the owner should establish who integrates those perspectives and who has authority when assumptions no longer hold. Contractual responsibility for a component does not automatically confer authority over the facility’s operating risk.
The maintenance package should make a few boundaries explicit:
- Who confirms that the starting configuration matches the approved plan?
- Who authorizes departure from that plan or stops the work?
- Who assesses the effect of control, firmware or settings changes?
- Who accepts the system back into normal service?
These are governance requirements, not substitutes for qualified personnel, approved safety procedures or statutory obligations.
Procurement also has a role. Where relevant, service scopes should include interface coordination, configuration records and return-to-service evidence. Buying only the physical task can leave the owner carrying the integration work without recognizing its cost or schedule impact.
Treat restoration as part of the work
A serviced asset is not necessarily a restored system. Local functional checks may show that equipment operates while leaving unresolved questions about load sharing, alarm routing, automatic response or interaction with adjacent systems.
Return-to-service criteria should be agreed before isolation begins. They should distinguish equipment completion from system acceptance. Appropriate verification depends on the asset, operating constraints and applicable safety requirements; not every condition can or should be demonstrated through a disruptive live test.
Where direct testing is constrained, the acceptance plan should identify alternative evidence, its limitations and any residual uncertainty requiring owner approval. A successful local test should not silently stand in for an unperformed system-level check.
Recovery also needs realistic treatment. Reversal may cease to be straightforward after disassembly, configuration changes or discovery of damage. The plan should identify those decision points and distinguish rollback from an alternative recovery route.
Finally, closeout should update the operating baseline. Revised settings, replaced components, remaining defects and changed dependencies belong in controlled records. Otherwise, the next maintenance window begins with assumptions that the previous one has already invalidated.
Questions owners should ask this quarter
The practical starting point is the next maintenance activity that changes the facility’s tolerance for failure. Ask for a concise statement of the temporary operating condition alongside the work order. It should connect the asset-level task to the services the business expects to remain available.
Owners can use the following questions at the approval gate:
- Does the plan reflect current demand and the actual configuration, rather than the original design alone?
- What additional failure would cause a service impact during this window?
- Which shared dependencies or concurrent activities could invalidate the plan?
- Who can stop the work, and what conditions require that decision?
- When does straightforward reversal cease to be available?
- What evidence is required before normal operation is accepted?
- Which risks remain after restoration, and who accepts them?
The resulting decision may be to proceed, change the scope or defer with explicit conditions. What matters is that maintenance approval becomes an operating decision supported by evidence. The work order authorizes a task. The owner must also authorize the system state around it.
Planning critical infrastructure?
Talk to the SHARE NET integration team about scope, architecture and delivery.
Further reading
Modular Infrastructure · 3 Oct 2026
Modular infrastructure: speed without shortcuts
Prefabrication can compress schedules, but only when integration and testing move into the factory too.
Read
Energy & BESS · 1 Oct 2026
BESS and the data center: beyond backup
Battery energy storage is moving from a resilience add-on to an active part of how critical facilities manage power.
Read
Critical Power · 28 Sept 2026
Power is the new constraint for AI compute
Why grid access, not silicon, increasingly decides where and how fast AI capacity can be deployed.
Read